trustyourinbox

Your DMARC toolkit. All in one place.

Identify your senders, fix configuration issues from the same screen, monitor changes, and connect your data to the tools you already use.

See who sends as you. By name, from your own reports.

Gmail, Microsoft, Yahoo and others send a daily report on the mail that used your domain. We read each one, name the senders we can, and put what needs you at the top of the dashboard.

The Start here card on the dashboard for kanbello.xyz: every identified sender aligned, 6,331 messages from sources we can't name to review before Reject, and what the replay found: unidentified sources, forwarded or mailing list, identified senders failing alignment.
_dmarc.kanbello.xyzApplied
Wasv=DMARC1; p=quarantine; rua=mailto:…
Nowv=DMARC1; p=reject; rua=mailto:…
  1. Staged, record emailed
  2. Held five minutes
  3. Written to Cloudflare
  4. Read back from DNS
The previous record is kept, so this change can be undone.Undo

Fix it from the same screen. See the exact change first.

When the fix is a DNS record, we can write it for you on Cloudflare and Route 53. The change waits five minutes, we email you the exact record, and once it is live we read it back from public DNS. On any other DNS host, you get the record and a link to the right page.

Watch for what changes. Alerts where you already work.

A critical finding reaches you in the app, by email, in Slack, or as a signed webhook to your own systems. The same finding won't repeat for fourteen days. In-app alerts are on every plan. Email starts on Lite, webhooks on Pro.

trustyourinboxin #security

shipfeat.ai: A lookalike domain has sent mail as you

View lookalikes
trustyourinboxEmail

shipfeat.ai: A lookalike domain has sent mail as you

WebhookPOST to your endpoint
X-TYI-Signature: sha256=9f1c…
{ "event": "anomaly.crit",
  "data": { "domainName": "shipfeat.ai" } }

Connect your data. The same numbers, outside the app.

Use the REST API in your own tools, ask Claude or Cursor about your domains over MCP, or run your clients' domains from a white-label console.

$ curl https://api.trustyourinbox.com/v1/domains \
    -H "Authorization: Bearer $API_KEY"
namestatuspurpose
shipfeat.aiverifiedsending
kanbello.xyzverifiedsending
pawpantry.exampleverifiedmonitor_only
Also over MCP, from ClaudeCursor or any MCP client.

Don’t take our word for it. Check the record.

DMARCv=DMARC1; p=reject; rua=mailto:…Reject
MTA-STSv=STSv1; id=… · policy mode: enforceEnforce
BIMIv=BIMI1; l=https://trustyourinbox.com/bimi/trustyourinbox-2026-11.svgPublished

Every price

Pricing
Free1 domain$0
Lite5 domains$9/mo
Pro25 domains$19/mo

Yearly $84 and $180. MSPs pay per domain.

All systems operational
Application6 of 6
Email pipeline4 of 4

Checked every 5 minutes. Nov 22, 20:35 UTC.

Shipped

Changelog
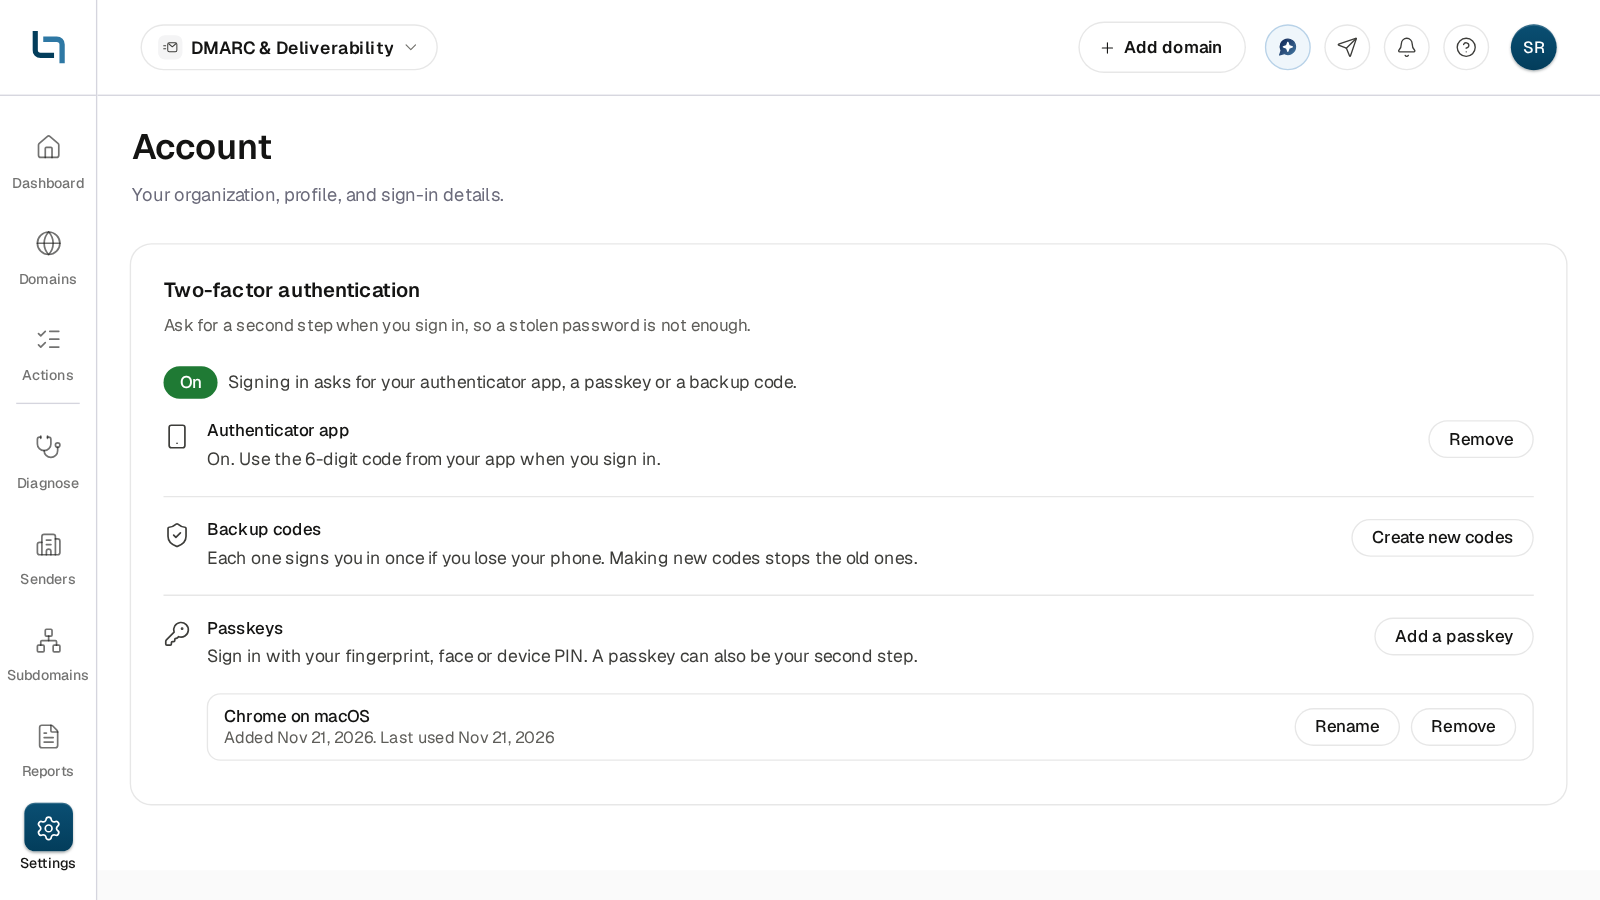
The Two-factor authentication card in Settings, Account, turned on with an authenticator app, backup codes and a passkey

Two-factor authentication and passkeys

Start with one domain. See it with your own data.

Free for one domain, no card. Add one DNS record and the first reports usually arrive within a day.

  1. Monitoring
  2. Quarantine
  3. Reject